
One secure platform to build, deploy, and operate.
IronSled brings GitLab, Rancher, AWS, and your security toolchain into a single portal — a clear, secure path from onboarding to production, so your team can ship without operating every system by hand.
Secure by default · CMMC-aligned environments · Built for tenant teams
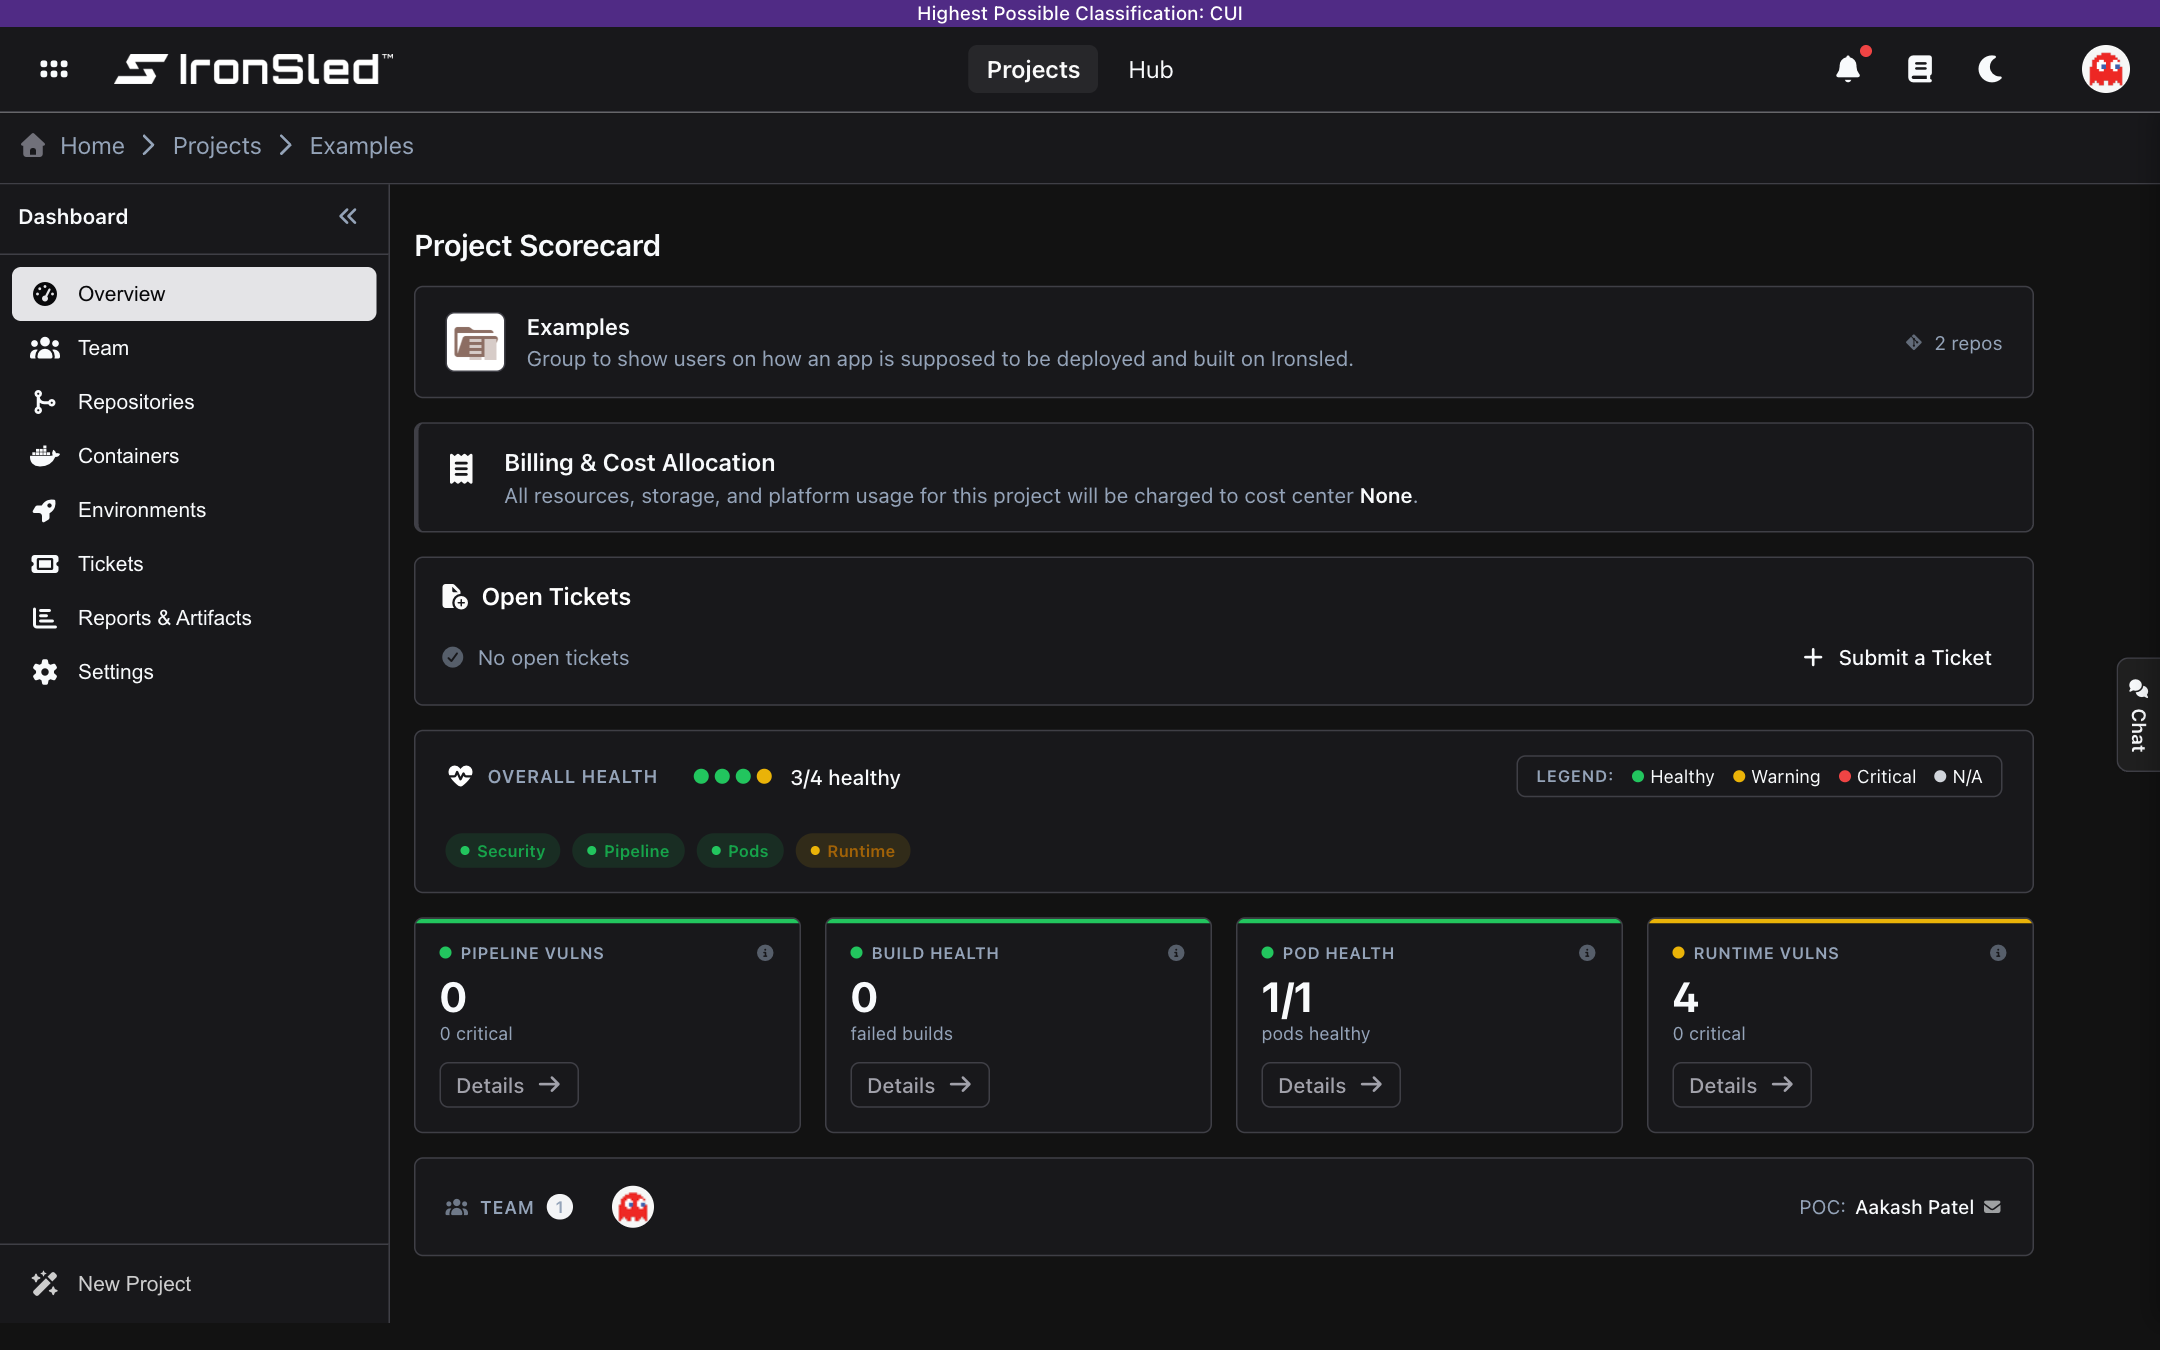
One portal, orchestrating your entire toolchain


The IronSled DevSecOps loop
Every IronSled project runs the same secure, GitOps-driven lifecycle. GitLab pipelines build images with Buildah, scan them with Trivy and Sonatype, and sign them with Cosign — then Rancher Fleet deploys to RKE2 clusters via Helm, with Grafana and NeuVector watching production. Security gates every stage, not just the end.
Everything your project needs, in one place
Manage repositories, environments, and security posture for every application from a single dashboard — no more jumping between tools.
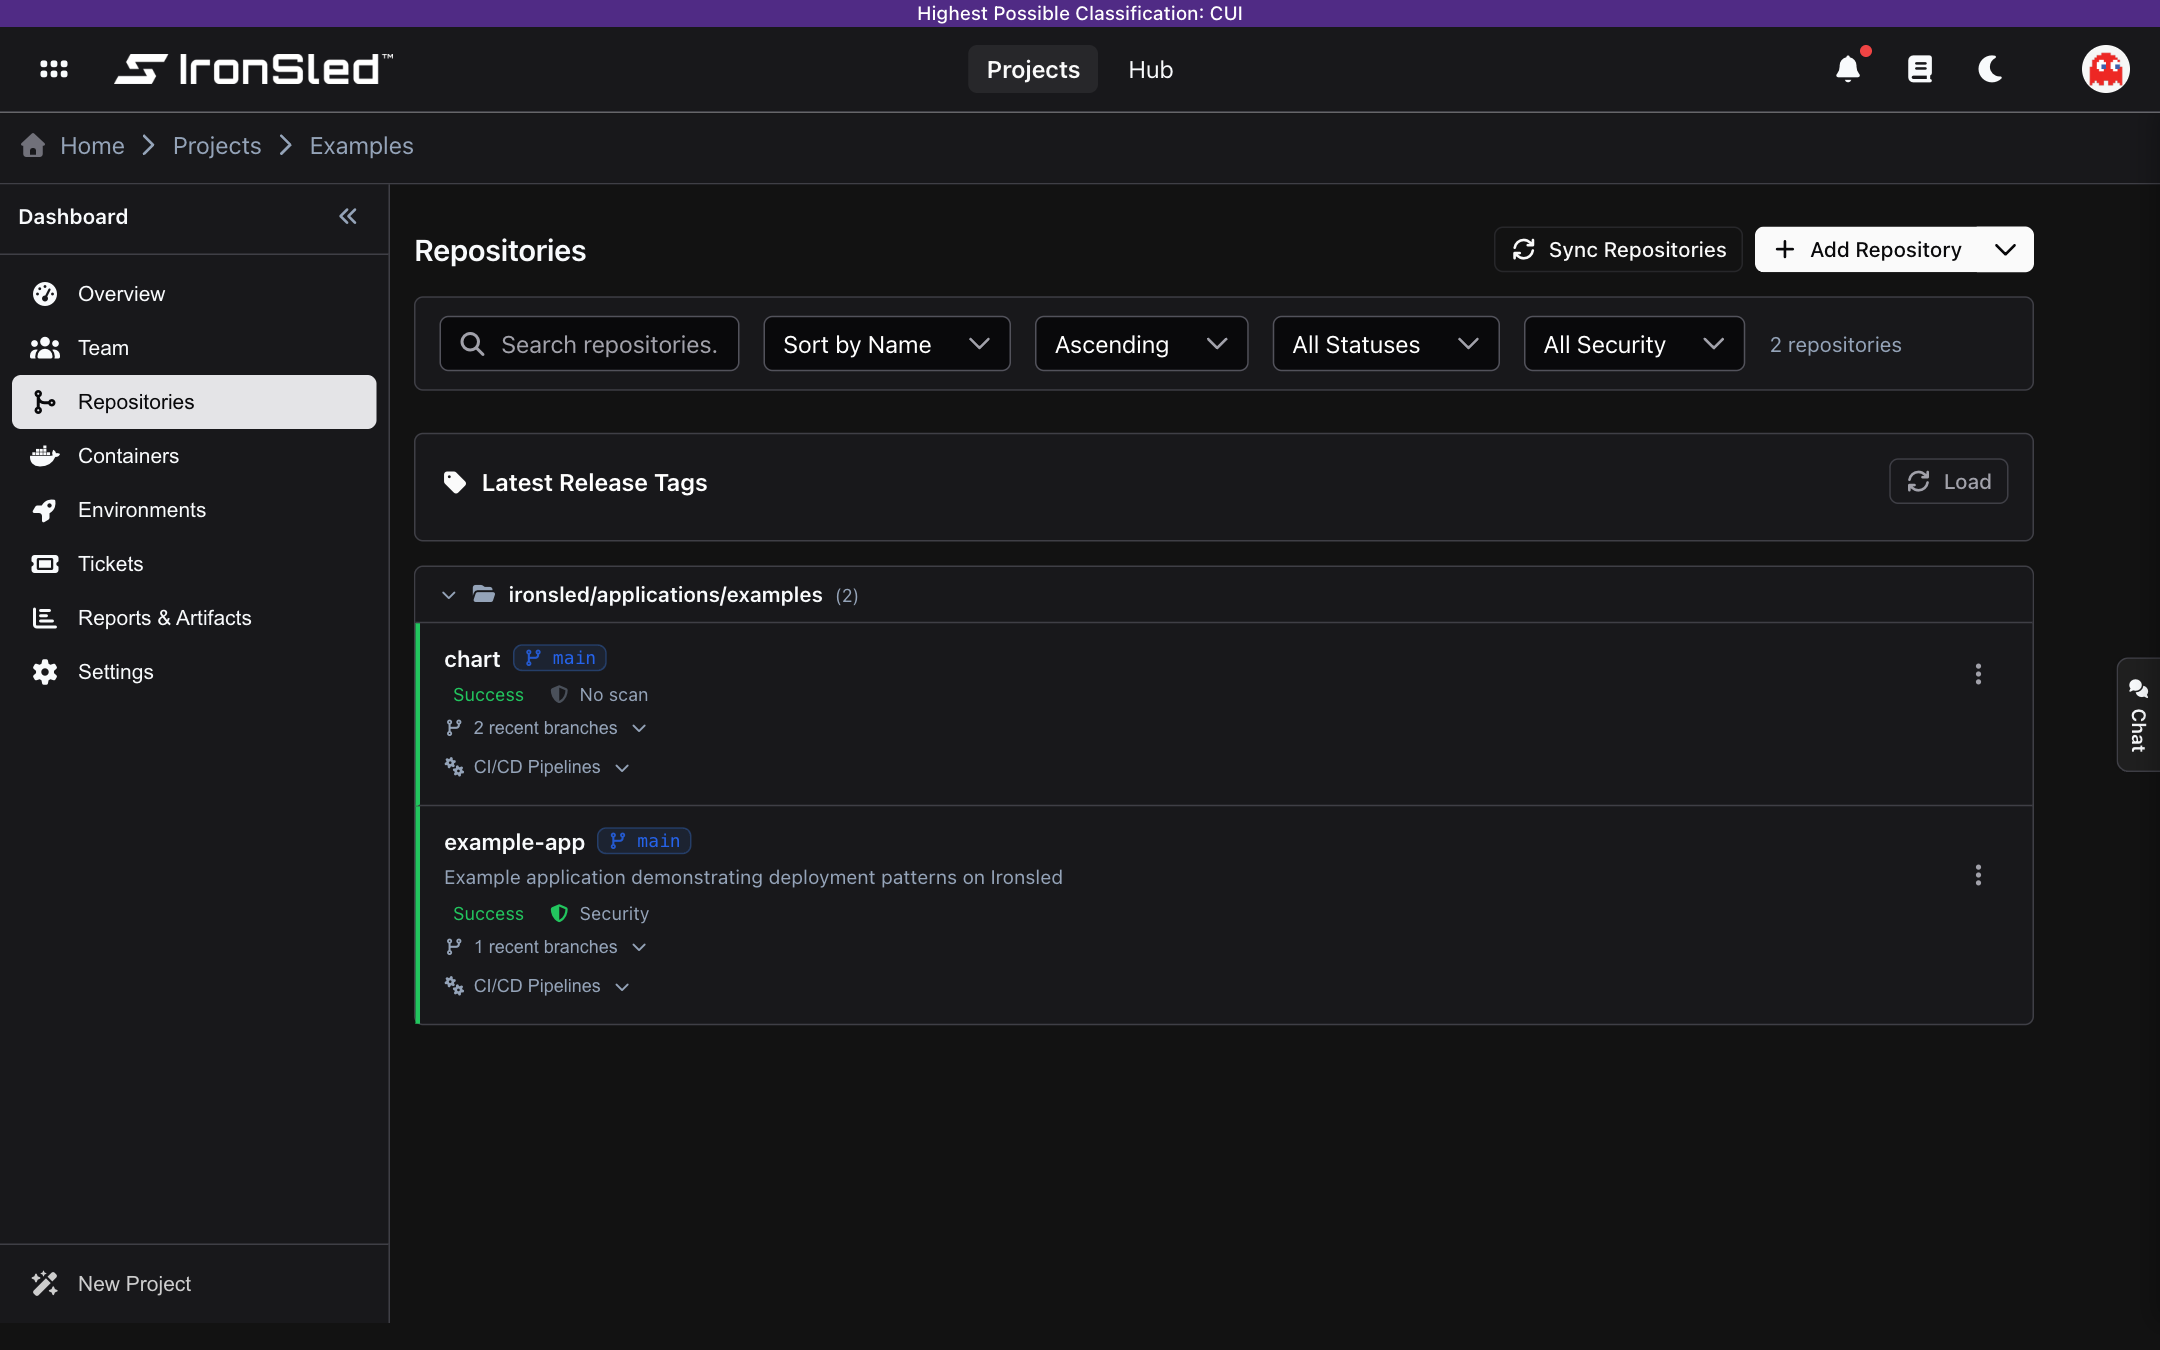
From repository to running container
Every project links your team to its GitLab repositories, branches, pipelines, and merge requests — with Trivy scan results, SBOMs, and release tags pulled in automatically. Versioning is handled for you: semantic-release follows your Conventional Commits to version, tag, and release every merge — no manual version bumps.
- Repositories, pipelines & merge requests
- Trivy scan results and SBOMs
- Automatic semantic versioning from commits
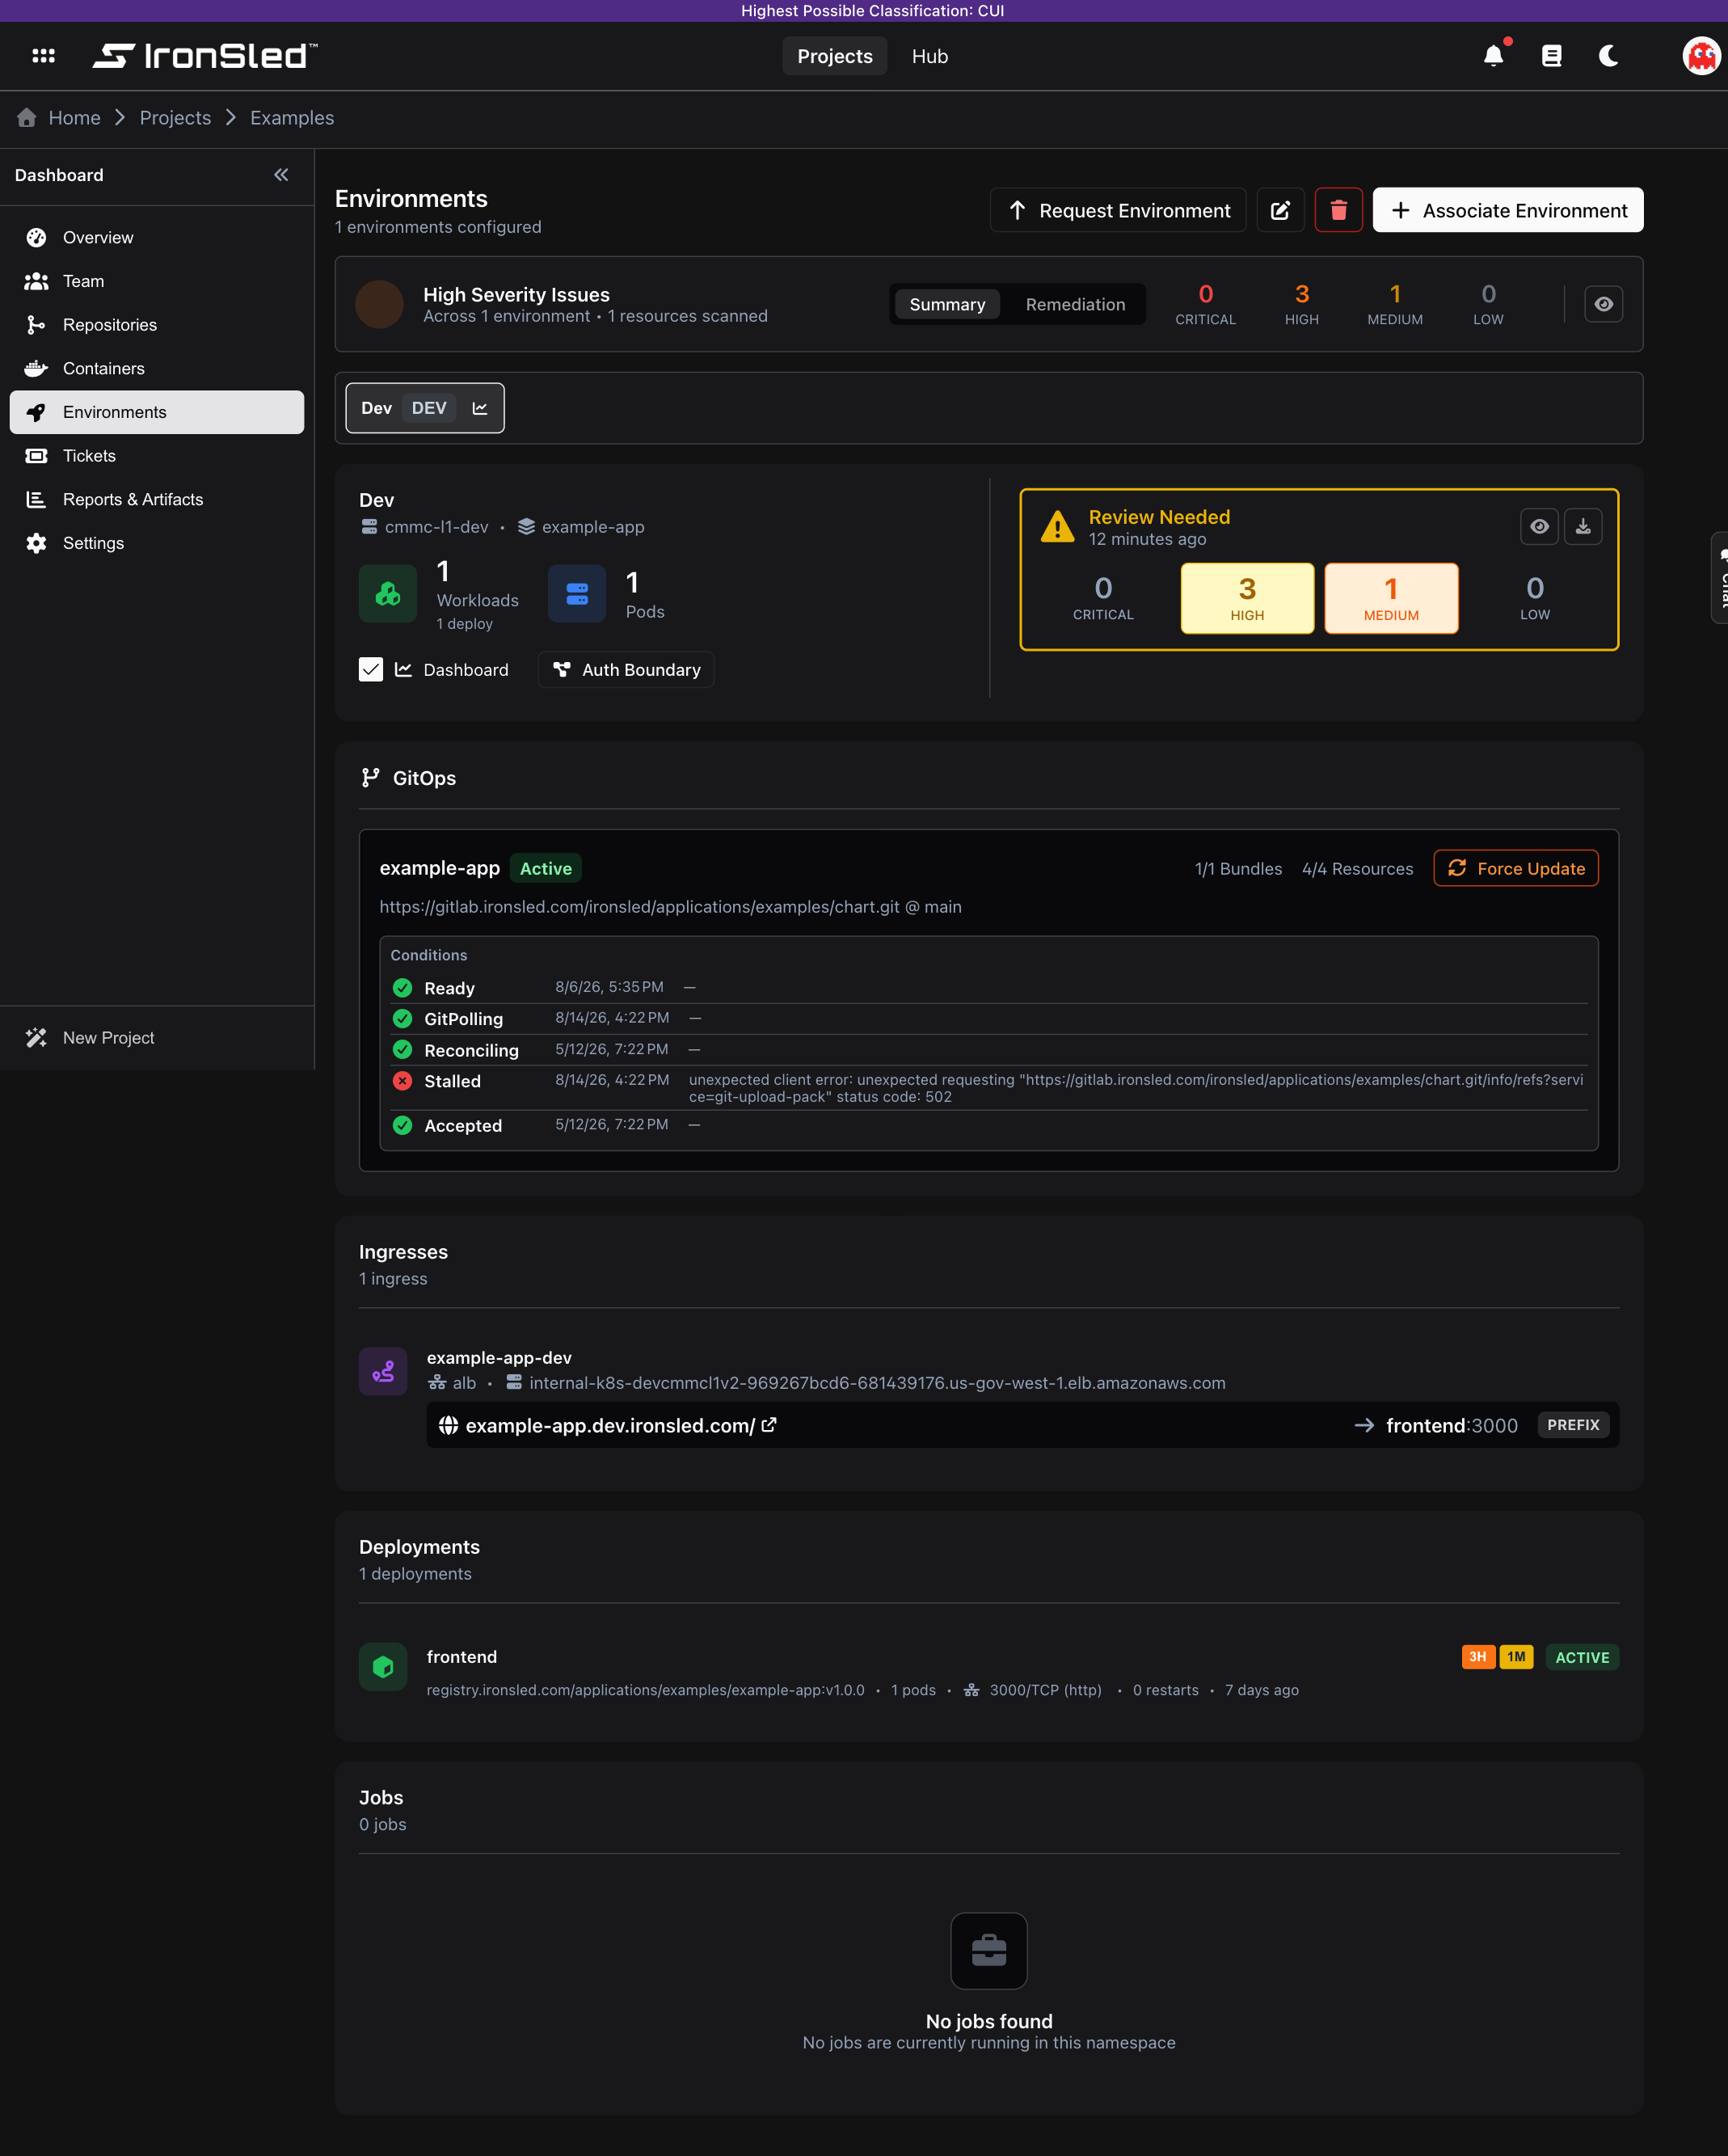
See what’s actually running
Environments map straight to your Kubernetes deployments in Rancher — workloads, pods, ingress, and live runtime security from the Trivy Operator, with deep links into Rancher when you need them.
- Kubernetes workloads, pods & ingress
- Runtime vulnerability findings
- One-click deep links into Rancher
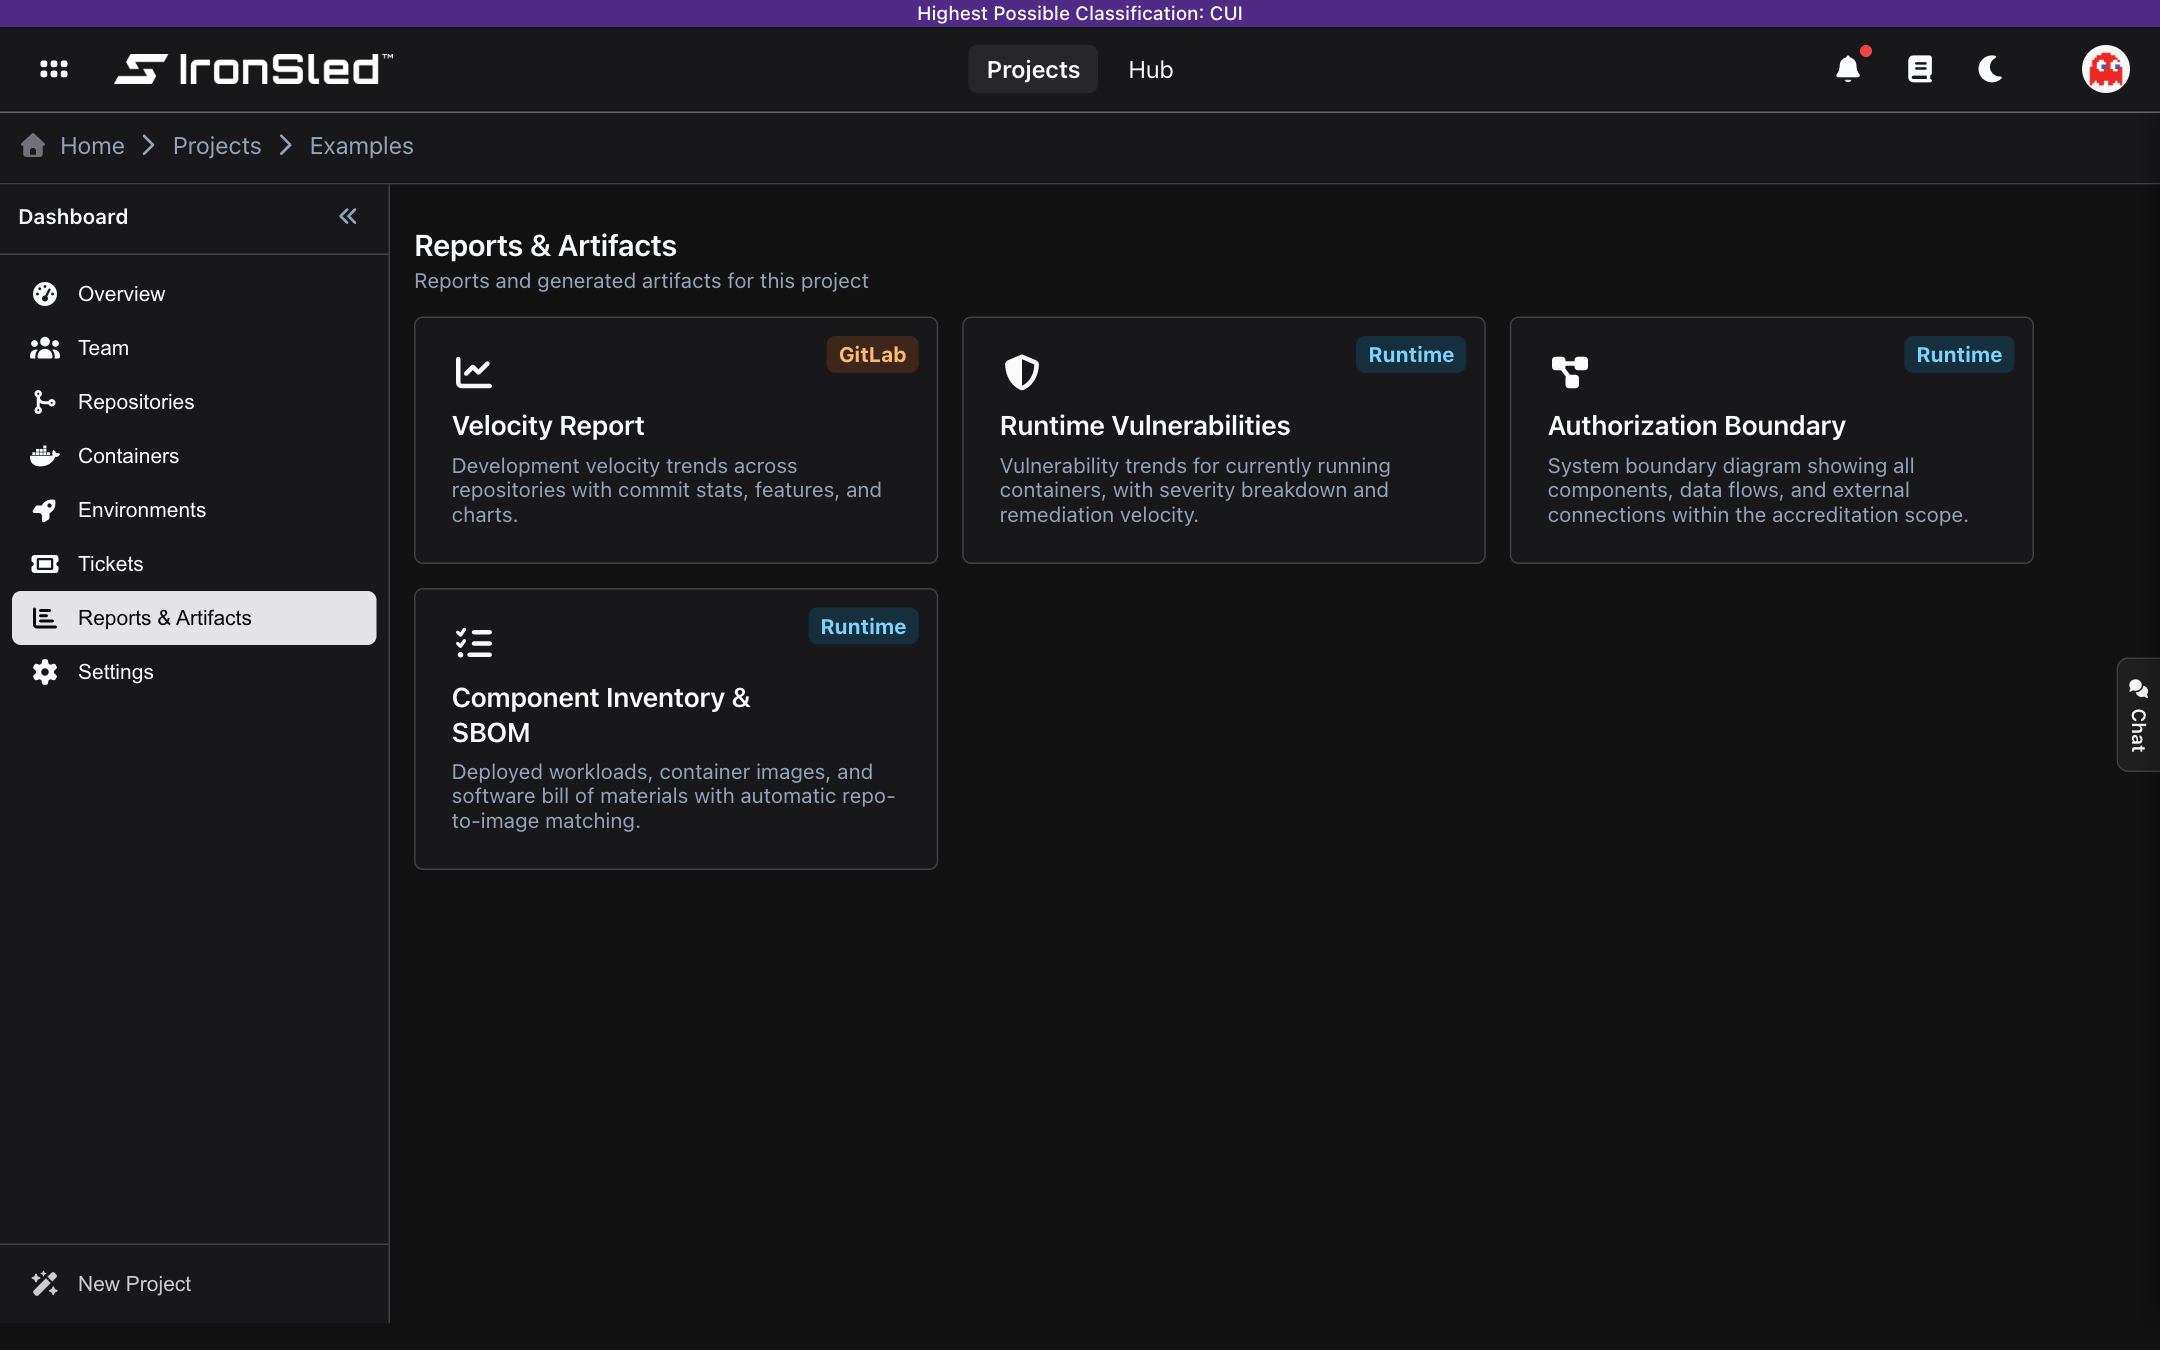
Security and compliance, built in
Generate velocity, vulnerability, and SBOM reports on demand — plus a Component Inventory of your project, all exportable to PDF, CSV, and JSON.
- Velocity & vulnerability reporting
- CycloneDX software bill of materials
- Component Inventory export
A PaaS should remove friction — and give teams a clear path to deliver with confidence.
Our mission is a secure, reliable, and user-friendly platform that helps tenant teams build, deploy, and operate applications faster — with clear standards, repeatable patterns, and the support to deliver with confidence.
Simplify application delivery
A clear, guided path from onboarding to production for every tenant team.
Secure, repeatable patterns
Hardened base images and standardized deployment patterns, secure by default.
Less tribal knowledge
Cut confusion and manual effort with documented, self-service workflows.
Consistent onboarding & support
The same reliable experience for getting started and getting help.
Standards that speed you up
Shared standards let teams move faster with confidence, not friction.
A platform teams trust
Built to be reliable, user-friendly, and one engineers actually want to use.
Dive into the documentation
Guides for everything you can do in the portal — from onboarding your first project to requesting infrastructure.
Projects
Project Onboarding
Tickets
Hub
Service Delivery
Ready to build on IronSled?
Start with the User Guide, or log in to the portal and open your first project.